Summary
Industrial devices with public static IP addresses are continuously scanned and targeted by attackers, and 2025–2026 data shows both ICS vulnerabilities and OT ransomware attacks rising sharply. The fix isn't giving up remote access — it's moving devices to a private network so there's no Internet-facing inbound exposure for attackers to find. Digi Axess VPN enables this by having devices initiate outbound-only encrypted cellular tunnels, so operators still get full remote visibility, direct device access, and centralized SIM/asset management without ever opening an inbound port or requiring a public IP. This architecture also aligns with IEC 62443 and NIST SP 800-82 Rev. 3 requirements and supports obligations under the EU Cyber Resilience Act, making it a relevant control for organizations tightening compliance postures.
If your industrial devices have a public static IP address, they are on the attack list. Here is what that means and how to fix it.
Most industrial teams spend a lot of time thinking about device configuration, uptime and field reliability. But how do those devices connect to the broader network, public or private, and protect device and information security? That single architectural decision shapes the entire security posture of a remote deployment. Key point: Organizations today must consider security at every point along the way.
The numbers make the case. ICS vulnerability disclosures nearly doubled in 2025, reaching 2,451, up from 1,690 the year before. Ransomware groups targeting industrial organizations surged 49% year-over-year, hitting more than 3,300 organizations globally.1 According to Palo Alto Networks' Intelligence-Driven Active Defense Report 2026, Cortex Xpanse recorded over 110 million observations of OT devices with Internet-facing inbound exposure in 2024 alone, a 138% increase over 2023.2
The answer is clear. Industrial devices belong on a private network, behind a firewall, with no Internet-facing inbound exposure. Here is what that protection actually delivers, and how Digi Axess VPN makes it practical at scale.
Scope note: This guidance applies specifically to devices using public static IP addresses or requiring inbound connections from third parties. Devices already on outbound-only cellular with no inbound exposure are in better shape, but a VPN still adds meaningful value for remote command-and-control, compliance documentation, and multi-site segmentation.
The Problem with Public Static IP Addresses on Industrial Devices
A public static IP address on an industrial controller or gateway is an open invitation to hackers. That is not a figure of speech. Internet-facing systems are continuously scanned by automated tools looking for open ports, known vulnerabilities and default credentials. The physical remoteness of a site provides no protection whatsoever. Once a device accepts inbound connections from a routable public address, it is reachable by anyone with an Internet connection, regardless of where it sits geographically.
Most industrial operators already know Internet-facing OT devices are a liability. The gap has never been awareness. It has been implementation. Setting up a more secure architecture has historically meant VPNs, VLANs, static routes, and a team with the expertise to manage all of it. For organizations without dedicated security staff, that cost and complexity has kept the public Internet as the path of least resistance, even when everyone in the room knows it should not be.
In April 2026, U.S. government agencies issued a joint advisory confirming that Iran-linked threat actors were actively exploiting Internet-facing programmable logic controllers (PLCs) in water and wastewater systems. The Darktrace assessment is blunt: Internet-facing control system components are "one of the clearest and most avoidable sources of OT risk." Avoidable, but only if the alternative is actually within reach.3
For industrial infrastructure (controllers managing pumps, valves and flow rates at unmanned sites), the consequences go beyond data loss. OT ransomware incidents caused partial operational shutdowns at 75% of affected industrial organizations in 2024, according to Dragos.1 When a controller goes offline or executes unauthorized logic, the impact is physical. Pumps stop. Valves fail. People notice.
The fix is straightforward. Move devices off the public Internet entirely. That does not mean giving up remote access. It means securing remote access through a private, encrypted network rather than exposing inbound ports to the open Internet.
What a Private Network Actually Protects
Moving devices to a private network is not just a checklist item. It changes the fundamental risk profile of a remote deployment. Here is what that shift actually protects against.
Eliminates Internet-Facing Inbound Exposure
Without a public static IP address, there is nothing for a scanner to find. Opportunistic scanning (the most common initial access vector in OT environments) depends on finding exposed services to probe. Remove the inbound exposure and you remove the entry point entirely. According to Nozomi Networks, more than half of organizations with OT environments remain insecurely connected to the Internet. Removing that exposure is still a differentiator, not the industry baseline.4
Keeps Operational Traffic Inside a Trusted Boundary
SCADA commands, sensor readings, firmware updates and configuration changes should never cross public networks unprotected. On a private network, that traffic stays within a defined, controlled boundary. Encrypted tunnels protect operational data even at the underlying cellular or wired transport layer. That layer matters more than most teams account for: over 60% of IoT devices currently transmit data without encryption, according to 2025–2026 threat intelligence data. When devices cannot protect their own traffic, the network has to.5
Enables Layered Access Control
On a private network, access is controlled at the network level before a user ever authenticates to the device itself. Only authorized users can reach the devices at all. That is a meaningfully different model than device credentials alone. NIST SP 800-82 Rev. 3 and IEC 62443 both require least-privilege access and strong authentication for remote OT access.6 You cannot enforce those controls on a device that anyone on the Internet can already reach. A private network provides the first layer of protection, while device-level controls add another layer by governing what authorized users can do once connected.
Digi Axess supports either multi-factor authentication (MFA) or single sign-on (SSO) per user, not both simultaneously. Each user is provisioned under one model. Role-based access control and device group scoping apply across both authentication paths, so access is always bounded by the user's defined role and the device groups they are authorized to reach.
Containing How Far an Incident Can Travel
Even well-secured environments experience incidents. The real question is how far an incident can travel, and that depends heavily on how the private network itself is architected. A properly segmented network can limit the scope of a compromise, so an issue at one remote site does not automatically create a lateral path to other sites or to enterprise IT systems. According to NCC Group, the industrial sector accounted for 29.6% of all ransomware activity in the 12 months to March 2026.7 Segmentation does not prevent incidents on its own. How it is designed determines whether one site becomes ten.
The Remote Access Objection (and the Right Answer)
Here is the objection we hear most often from organizations evaluating private networks: "We need to access these devices remotely. If they are not Internet-facing, how do we manage them?"
It is the right question. The wrong answer is a public static IP address with inbound ports open. The right answer is a purpose-built VPN that gives you all the operational access you need without exposing any device to unsolicited inbound traffic.
Digi Axess VPN is built specifically for distributed industrial deployments. Devices initiate an outbound connection over cellular on an encrypted private network tunnel. No inbound port is ever opened. No publicly routable address is required. Authorized users reach devices through the platform, not through an Internet-facing address. Remote access happens through the private tunnel, not around it.8,9
What Digi Axess VPN Makes Possible
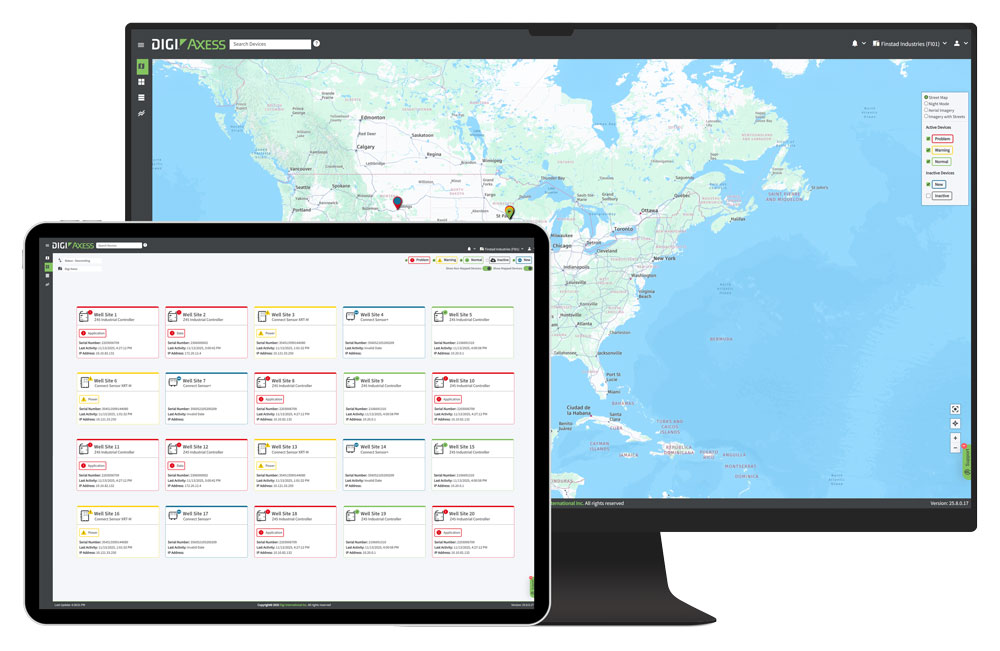 Moving to a private network model with Digi Axess VPN does not reduce what your team can do. It extends it, without the overhead of managing public static IP addresses across a distributed fleet.
Full Remote Visibility Without Public Exposure
Digi Axess VPN provides centralized monitoring for distributed industrial deployments: threshold breach alerts, fleet-wide comparisons and operational overviews, all accessible through the platform. No direct, Internet-facing inbound path to any device required. Your team gets the visibility it needs. The devices stay off the public Internet entirely.10
Secure Direct Device Access via VPN Link
VPN Link gives authorized operators direct web UI access to connected devices from within the Digi Axess platform, with no separate VPN client software, no public static IP, and no port forwarding. Access is authenticated, logged and bounded by role-based permissions. When a technician needs to reach a controller at a remote unmanned site, they get there through the private tunnel. No permanent inbound exposure is created.10
Carrier-Level Network Resilience
For remote sites where a technician dispatch means hours of drive time and real cost, network resilience matters. The Digi Mobile Private Network (MPN) service provides failover with each carrier, helping maintain connectivity through disruptions without requiring operator action. That resilience operates at the carrier and network level. The private tunnel itself stays closed to outside access throughout.11
Centralized SIM and Asset Management
The June 2026 Digi Axess platform update added centralized SIM management (ICCID, IMEI, IP address and account-level SIM details) directly into the platform for Digi data plan customers. Inventory updates automatically when devices connect or disconnect. If you are managing dozens or hundreds of remote sites, that replaces manual spreadsheet tracking with automated visibility and makes it faster to identify devices that are offline or behaving unexpectedly.10
Several of these capabilities are made possible by end-to-end ownership of hardware, cellular SIM, private network and cloud infrastructure. That is a stack no patchwork of third-party tools can replicate.
Compliance: Why the Architecture Decision Matters Now
The architecture decision is not just operational. It is directly relevant to the compliance requirements that industrial teams are increasingly expected to meet, and that regulators are increasingly scrutinizing.
IEC 62443, the international standard for industrial automation and control system cybersecurity, points to network segmentation through a zone-and-conduit model, encrypted communications, and role-based access control for remote sessions. NIST SP 800-82 Rev. 3, the U.S. federal guide for OT security, explicitly maps to IEC 62443 and requires least-privilege access and strong authentication for remote OT access. Both frameworks point to the same architectural reality: OT environments that are not segmented from external networks carry a fundamentally higher risk profile. That is not an opinion. It is the framework position.6
Digi Axess VPN supports the architectural controls these frameworks point to: encrypted communications, outbound-only tunnel architecture, and controlled remote access. It does not certify or guarantee your organization's compliance outcome; your team owns that. For deployments requiring dedicated network segmentation to satisfy zone-and-conduit requirements, Digi can support that configuration. Contact your Digi representative to discuss deployment options.8
The EU Cyber Resilience Act (Regulation EU 2024/2847) adds a binding regulatory layer. As of September 11, 2026, manufacturers of connected products sold into EU markets must report actively exploited vulnerabilities to ENISA within 24 hours. Full conformity requirements, including security by design and documented vulnerability management, apply from December 11, 2027. For industrial operators managing OT equipment in EU markets, a private network architecture with controlled remote access is directly relevant to demonstrating those obligations.12,13
Organizations that have already moved to a private network model (with encrypted tunnels, role-based remote access and centralized asset management) are typically better positioned when assessments come. One architectural decision supports multiple framework requirements at once, rather than requiring point-by-point control implementation after the fact.
Getting Started with Digi Axess VPN
Digi Axess VPN works with existing hardware. There is no infrastructure overhaul required to move your devices off the public Internet. All you need is an outbound-only encrypted cellular tunnel, a platform to manage through, and a firewall that stays closed.
Every day a remote OT device sits on a public static IP with inbound ports exposed is a day it is on the scan list.1,2 To learn more or request a demo, visit the Digi Axess page or contact Digi at digi.com/contactus.
Frequently Asked Questions About Private Networks and VPN
What is Digi Axess VPN?
Digi Axess VPN is a private virtual network service from Digi International designed for distributed industrial deployments. It enables remote devices to communicate over outbound-only encrypted cellular tunnels without requiring public static IP addresses, eliminating the Internet-facing inbound exposure that makes OT systems a target.
Why do IIoT devices belong on a private network instead of the public Internet?
Devices with public static IP addresses that accept inbound connections are continuously scanned by automated tools looking for open ports and known vulnerabilities. ICS vulnerability disclosures nearly doubled in 2025, and OT ransomware attacks surged 49% year-over-year.1 A private network removes Internet-facing inbound exposure entirely, the most effective single architectural control available to industrial operators.
Does Digi Axess VPN require a public static IP address?
No. Digi Axess VPN eliminates the need for public static IP addresses. Devices initiate an outbound connection over cellular on an encrypted private network tunnel. No inbound port is ever opened, removing that exposure point from the attack surface entirely.8,9
Can operators still access devices remotely when they are on a private network?
Yes, if they are using a solution like Digi Axess. Digi Axess VPN Link gives authorized operators direct web UI access to connected devices from within the Digi Axess platform; no separate VPN client is required. All access is authenticated, role-based and logged. Remote access is fully preserved; it happens through a private, encrypted tunnel rather than an Internet-facing inbound connection.10
How does Digi Axess VPN support IEC 62443 and NIST SP 800-82 compliance?
Digi Axess VPN supports the architectural controls these frameworks require: encrypted communications, outbound-only tunnel architecture that eliminates Internet-facing inbound exposure, and controlled remote access with role-based permissions. It supports the architecture IEC 62443 and NIST SP 800-82 Rev. 3 point to; your organization owns its compliance outcome. For deployments requiring dedicated network segmentation to satisfy zone-and-conduit requirements, contact your Digi representative to discuss deployment options.6
What authentication options does Digi Axess support?
Digi Axess supports either multi-factor authentication (MFA) or single sign-on (SSO) per user, not both simultaneously. Each user is provisioned under one model. Role-based access control and device group scoping apply across both authentication paths.8
What industries does Digi Axess VPN support?
Digi Axess VPN is designed for any team managing distributed industrial devices at remote or unmanned sites: water and wastewater, oil and gas, industrial automation, manufacturing, environmental monitoring and smart infrastructure. Any environment where physical remoteness has historically been treated as a substitute for network security is a direct fit.8
What is a private network in industrial IoT?
A private network restricts connectivity to authorized devices, users, and systems, so devices are not directly reachable from the public Internet. In carrier-provided industrial deployments, devices connect over a segmented cellular path without public IP addresses or Internet-exposed inbound ports. Access is controlled through designated gateways and security policies.
What is the difference between a private network and a VPN?
A private network limits who and what can connect. A VPN provides encrypted connectivity between authorized endpoints, including over shared infrastructure such as the Internet. Industrial teams often combine them: private networking prevents direct public access to devices, while a VPN provides secure remote access.
Is carrier private cellular connectivity the same as a VPN?
No. Carrier private cellular connectivity, such as a private APN, uses network segmentation and controlled routing to separate device traffic from general Internet access. A VPN adds encryption between its endpoints. Together, they provide complementary protection through network isolation and encrypted connectivity.
Why do IIoT devices need industrial remote access instead of a consumer VPN?
Consumer VPNs primarily route users' Internet traffic through a provider's servers for privacy. Industrial remote-access solutions provide controlled access to operational devices and support managing unattended fleets.
Industrial deployments need capabilities such as role-based technician access, centralized device grouping, audit logging, and outbound-initiated device tunnels where needed. The exact requirements depend on the network architecture and operational needs.
Is a private network more expensive than a public IP setup for industrial devices?
Not necessarily. Public static IP addresses may carry ongoing carrier fees, while private connectivity services have their own subscription and management costs. The comparison should include setup, administration, security controls, and potential downtime, not just connectivity charges. Depending on the deployment, a single incident's downtime, response, and remediation costs can outweigh the difference in connectivity costs.
Digi Axess VPN combines cellular connectivity and private remote access to simplify deployment and ongoing management. Actual savings depend on the service plan, fleet size, and existing infrastructure.
Do private networks eliminate the need for device-level security?
No. A properly configured private network prevents direct inbound Internet access to devices, but compromised accounts or connected systems can still create attack paths. Authentication, credential management, patching, and least-privilege access remain essential. Private networking limits exposure; device-level controls help prevent unauthorized access and limit damage if a compromise occurs.
Resources
1 Dragos, "OT Cybersecurity Year in Review 2024 / 2025," Industrial Cyber summary: industrialcyber.co
2 Palo Alto Networks, "Intelligence-Driven Active Defense Report 2026," via Help Net Security: helpnetsecurity.com
3 Dark Reading / Darktrace, "Industrial Controllers Vulnerable as Conflicts Move to Cyber" (April 2026): darkreading.com
4 Nozomi Networks OT exposure data, via Industrial Cyber / Canadian Cybersecurity Network Report: industrialcyber.co
5 Cybelangel / ZeroThreat, "IoT Cybersecurity: Unencrypted Traffic Statistics 2026": cybelangel.com
6 ShieldWorkz, "Using the IEC 62443 Framework to Comply with NIST SP 800-82: A CISO's Guide" (February 2026): shieldworkz.com
7 NCC Group, "Industrial Sector Ransomware Targeting 2025–2026," Automation.com (May 2026): automation.com
8 Digi International, Digi Axess VPN product page: digi.com
9 Control Global, "Digi Launches Mobile App and VPN for Infrastructure": controlglobal.com
10 Digi International, "Digi Expands Digi Axess Platform with Native Remote Access, SIM Management and Advanced IoT Analytics," BusinessWire (June 11, 2026): businesswire.com
11 Digi International, Digi Axess VPN datasheet: digi.com
12 BrightDefense, "EU Cyber Resilience Act — September 2026 Reporting Deadline" (May 2026): brightdefense.com
13 Cloudsmith, "The EU Cyber Resilience Act: What Engineering Teams Need to Do to Be Compliant" (June 2026): cloudsmith.com